WHO THIS IS FOR
Most procurement reviews of video analytics stall on one question from the data protection officer: where does the footage go? With an edge appliance, it goes to a box in your own comms room. That answers the residency and cross-border transfer questions in UK GDPR, Singapore’s PDPA, Australia’s Privacy Act and the UAE’s PDPL before anyone has to draft a transfer agreement. It does not settle lawful basis, signage, impact assessments or retention, and this article covers both halves.
THE QUESTION
What Data Residency Rules Actually Ask Of A Video System
Data residency rules ask whether personal data leaves the country, and who receives it on the other side. Camera footage of identifiable people is personal data in all four regimes below. A cloud analytics service that streams that footage to another jurisdiction therefore triggers a transfer regime. An appliance that analyses the stream on site and keeps the results there does not.
The UK regulator says this directly. The ICO’s video surveillance guidance treats CCTV images, vehicle registrations read by ANPR, and facial recognition outputs as personal data. It describes surveillance as acceptable only where it is lawful, necessary and proportionate. Where the processing happens matters because every transfer adds a second set of obligations on top of the first.
The United States has no federal equivalent of these regimes. The pressure there comes from state law, with Illinois’s Biometric Information Privacy Act the statute most often litigated over face data. The rest of this article concentrates on the four markets with explicit transfer rules.
MARKET BY MARKET
How Four Privacy Laws Treat Footage That Crosses A Border
Each of the four laws restricts sending personal data abroad, and each one leaves the obligation with the organisation that collected it. The table summarises what a transfer would trigger and what the maximum exposure looks like.
| Jurisdiction | Law | What A Transfer Triggers | Maximum Penalty |
|---|---|---|---|
| United Kingdom | UK GDPR and Data Protection Act 2018, as amended by the Data (Use and Access) Act 2025 | A restricted transfer needs adequacy regulations or safeguards, plus a documented test that protection abroad is not materially lower | £17.5 million or 4% of worldwide annual turnover, whichever is higher |
| Singapore | Personal Data Protection Act 2012, section 26 | Transfer only where the recipient is bound to protection comparable to the PDPA | S$1 million, or 10% of Singapore turnover where that turnover exceeds S$10 million |
| Australia | Privacy Act 1988, APP 8 and section 16C | Reasonable steps before disclosure, and the Australian entity stays accountable for the overseas recipient’s breaches | The greater of A$50 million, three times the benefit, or 30% of adjusted turnover |
| UAE (onshore) | Federal Decree-Law No. 45 of 2021 (PDPL), Articles 22 and 23 | Transfer to an adequate jurisdiction, or under listed exceptions such as contract or express consent | Set by implementing Cabinet decisions |
A few details matter for video in particular. The ICO’s January 2026 update to its international transfers guidance, summarised by Kennedys, states that an overseas contractor with remote access to UK data is making a restricted transfer. Remote viewing therefore counts, and no file has to be copied abroad for the rules to apply.
Australia’s rule is the strictest in practice. The OAIC’s APP 8 guidelines explain that the Australian entity is treated as having committed an overseas recipient’s breach itself, even where it took reasonable steps beforehand. The penalties are no longer theoretical. In 2025 the Federal Court ordered Australian Clinical Labs to pay A$5.8 million, which Lavan reports was the first civil penalty under the Act.
The UAE needs a further check. Entities in the DIFC and ADGM free zones fall under those zones’ own data protection laws, which have their own transfer rules. The federal PDPL has been in force since January 2022, but practitioner sources still disagree about whether its full executive regulations have been published. Check the current position with counsel before relying on a specific procedure. Keeping the data in the building avoids most of that uncertainty.
WHERE THE VIDEO GOES
What Stays On Site With An ARSA AI Box
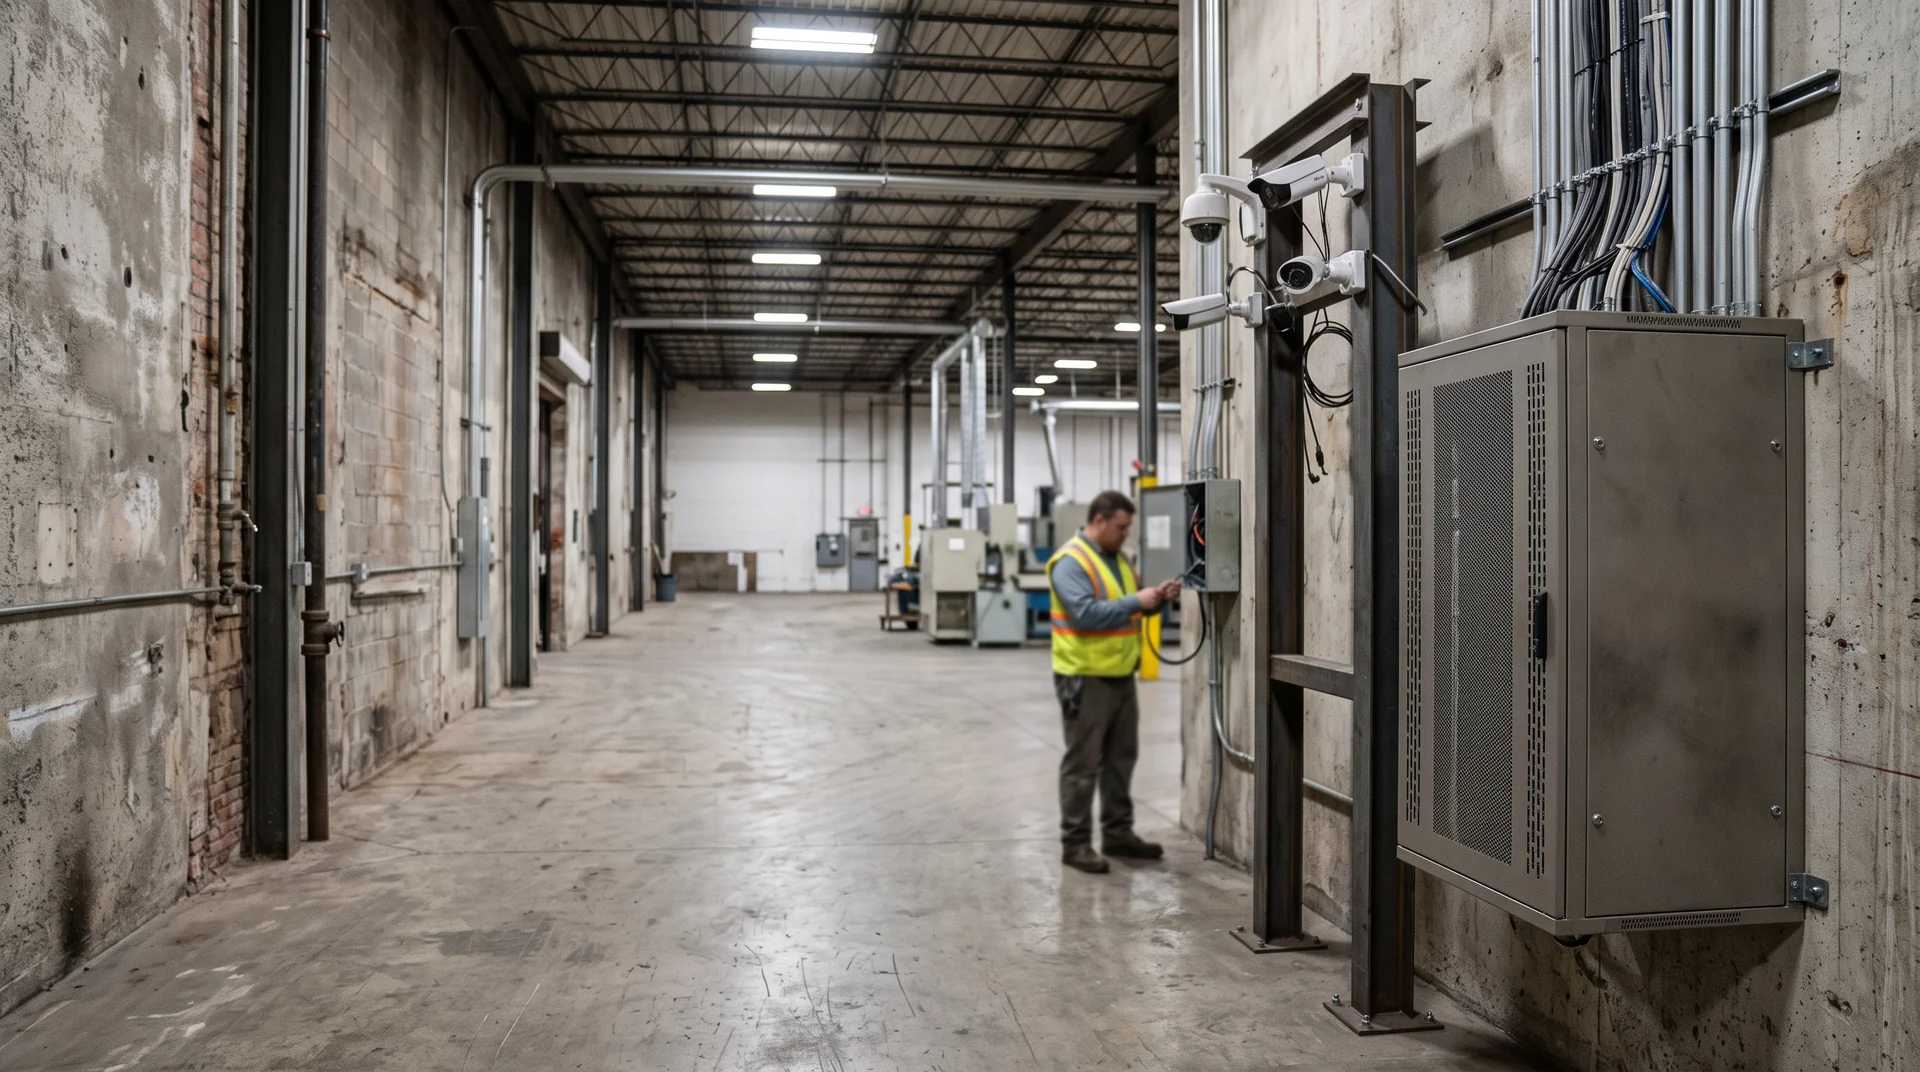
With the ARSA AI Box Series, every stage of analysis runs on the appliance at your site, and nothing leaves your network unless you configure a route out. Cloud connectivity is optional and off by default, and ARSA does not operate a cloud inference service. The appliance runs detection, alerting and its local dashboard with no internet connection at all.
| Data | Where It Lives | Who Controls It |
|---|---|---|
| Live camera streams | Your camera network, read by the appliance over ONVIF or RTSP | You |
| Recorded video | Your existing VMS or NVR; the AI Box does not record | You |
| Event metadata and detection snapshots | Stored locally on the appliance | You |
| Alerts | Local dashboard, or a webhook, email or alerting stack you choose | You choose the destination |
| Licence activation and model updates | Online, or as offline packages for air-gapped sites | You decide whether the unit connects |
The appliance comes in two sizes. The Mini PC model handles up to three cameras and the Server model up to 25, so one unit can cover a whole site from a comms room. For organisations that already run GPU servers, the AI Video Analytics Software runs the same analytics as containers on your own hardware, with streams, inference results and metadata staying inside your infrastructure.
The camera network matters too. ARSA’s site standard calls for cameras on an isolated VLAN, which keeps the video path separate from the corporate network and from the internet. The full requirements are in the system requirements.
THE HONEST EDGES
Three Ways Data Can Still Leave The Building
On-premise processing keeps data on site only if the routes out stay closed. Each of the three routes below is something you configure, and each one is worth recording in your transfer register if you open it.
Alerts You Route Outward
An alert sent to a hosted email service or a cloud messaging tool can carry a detection snapshot with a person in it. If that service stores the message in another country, you have made a transfer. Route alerts to systems inside your own estate, or check where your alerting provider keeps its data.
Remote Support Sessions
Remote support needs connectivity, and ARSA’s engineers are based in Indonesia. If a support session can see snapshots or live streams, the UK, Singapore and Australia would all treat that access as a transfer. Give access case by case under a written agreement, or keep the unit offline and handle support without access to footage.
Model And Licence Updates
Updates pulled over the internet need an outbound connection. Air-gapped sites can avoid that entirely, because licence activation and model updates are both available as offline packages, moved in on your own approved media.
WHAT REMAINS YOURS
The Obligations Edge Processing Does Not Remove
Edge processing settles the location question. It leaves the rest of each privacy law in place, and a regulator will still ask about all of it. You still need a lawful basis for each analytic you switch on, and visible notice before people walk into view. Singapore’s PDPC, for example, recommends signs at building entrances and in prominent locations, readable before the camera captures anyone.
Impact assessments still apply as well. Under UK GDPR, systematic monitoring of a publicly accessible area generally requires a data protection impact assessment. Australia’s privacy regulator found against Bunnings in 2024 over facial recognition in its stores. That case turned on notice and consent, and the processing being local did not help. Some analytics carry more weight than others. PPE detection looks for helmets and vests. Demographic estimation for screen audiences and live number plate reading still involve identifiable people or vehicles, so each needs its own justification.
Retention and access requests remain your responsibility, through the VMS or NVR that holds your recordings. Ask ARSA how long detection snapshots are kept on the appliance and how you can export or delete them on request, then write the answer into your retention schedule. ARSA does not claim any certification that would do this work for you.
BUYING FROM ABROAD
Deploying In The UK, Singapore, Australia Or The UAE
ARSA sells the AI Box and the video analytics software outside Indonesia. International list prices are in USD, invoicing is available in USD or EUR, and an appliance ships from Surabaya in three to four weeks. Import duty, VAT and customs clearance are the buyer’s responsibility. Where visa conditions prevent ARSA engineers from travelling, a qualified local partner installs under ARSA supervision.
Existing cameras usually work if they meet the minimum of 2 MP at 15 fps, with 4 MP recommended. A Remote Camera Design Review costs $1,500, takes one week and returns a pass or fail for every camera position. For larger sites, an On-Site Camera Survey costs $4,500 plus travel and covers up to 50 cameras. Either fee is deducted from the project fee if you contract within 90 days. Both are listed under services.
FAQ
Frequently Asked Questions
Does On-Premise AI Video Analytics Satisfy UK GDPR?
It satisfies the international transfer rules, as long as no footage, snapshot or remote access crosses the border. UK GDPR still requires a lawful basis, signage, a data protection impact assessment where monitoring is systematic, and a retention policy. Processing on site makes that work smaller and does not replace it.
Is Sending CCTV Footage To A Cloud Service A Cross-Border Transfer?
It is whenever the provider stores or processes the footage outside your country. The UK, Singapore, Australia and the onshore UAE all then require safeguards, such as adequacy, contracts or consent. In Australia, the accountability under section 16C stays with you even after you have taken those steps.
Can An ARSA AI Box Run Fully Air-Gapped?
Yes. Detection, alerting and the local dashboard all run offline, and licence activation and model updates come as offline packages. The trade-off is that remote support also needs connectivity, so support at an air-gapped site happens without remote access.
Does The AI Box Store Video Recordings?
No. The AI Box analyses live streams, and recording stays with your existing VMS or NVR. The appliance stores event metadata and detection snapshots locally. Those snapshots are personal data and belong in your retention schedule.
Do DIFC And ADGM Companies Follow The UAE PDPL?
Generally no. Entities licensed in those free zones fall under the DIFC Data Protection Law and the ADGM Data Protection Regulations, each with its own transfer rules. Processing on site keeps you clear of both sets of transfer rules, so confirm which regime applies to you before the impact assessment.
NEXT STEP
See Where Your Video Stays
If your compliance review keeps returning to where the footage goes, start with an appliance that keeps every stage of analysis inside your own network. Compare the Mini and Server models, both buying options and the full data flow on the ARSA AI Box Series page.